
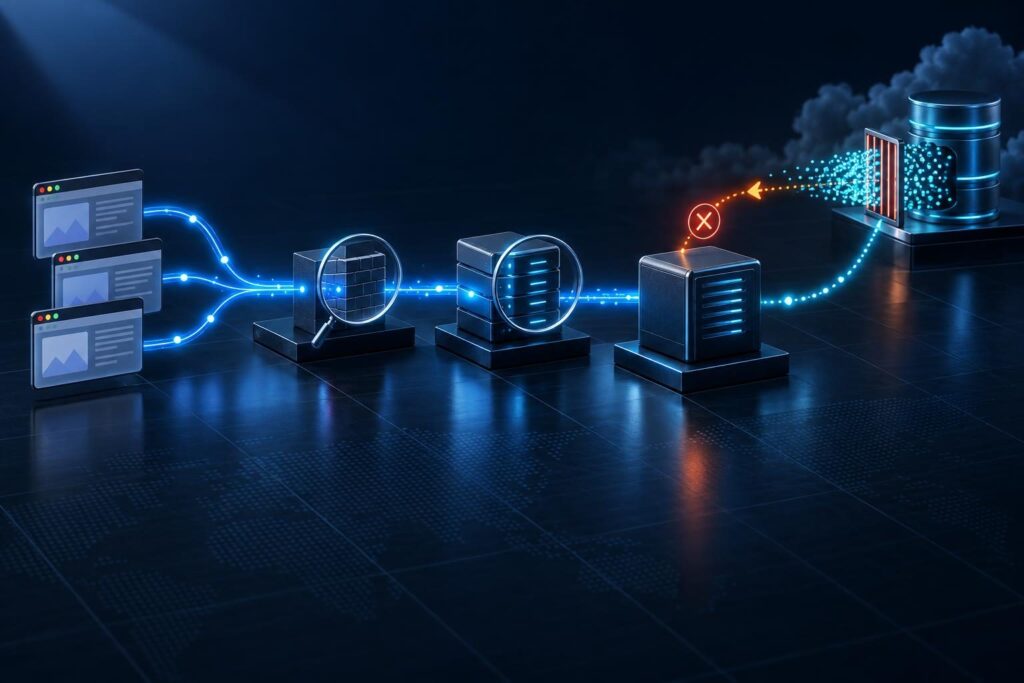
A 429 Too Many Requests response usually signals website rate limiting, but it does not identify the responsible system. Your hosting provider, a security service, WordPress code, or an external service may enforce the limit. Repeated refreshes can extend the disruption or add more traffic.
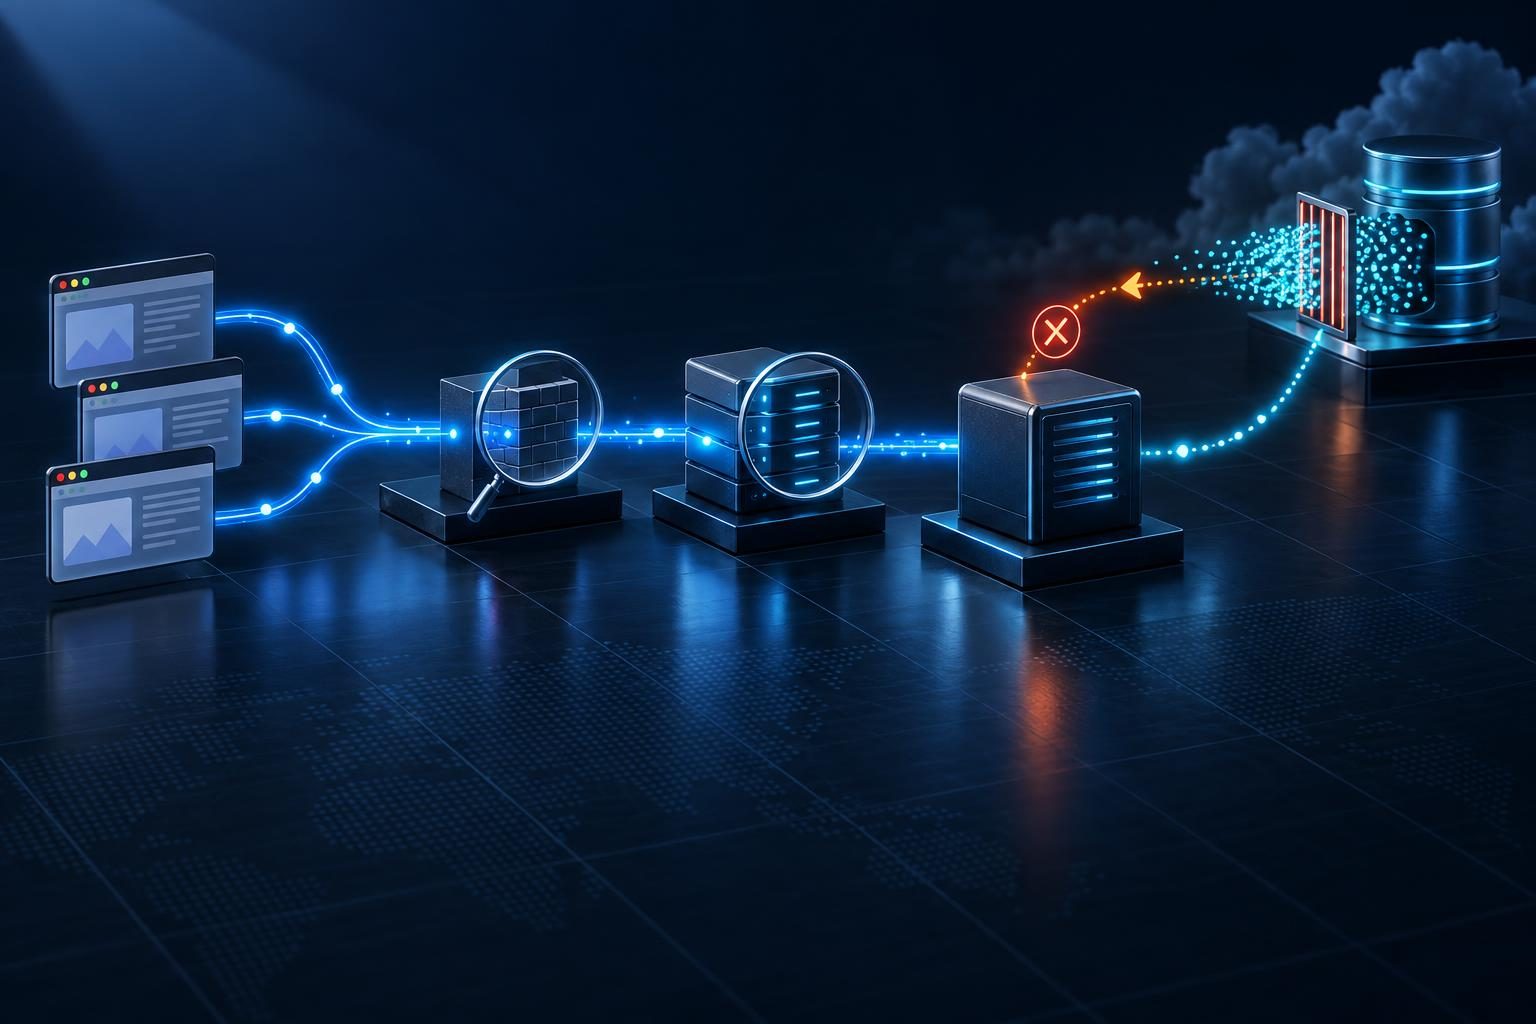
The practical goal is to identify who rejected which request, and why. Then reduce unnecessary demand or adjust a narrowly defined policy. This approach helps protect bookings, tenant portals, checkout pages, and staff tools without weakening security.
What a 429 Response Actually Tells You
HTTP is the protocol browsers use to request web content. Its 429 status means the responding system considers the request rate too high. However, each system defines its own counting rules.
A limit might apply to an IP address, user account, session, application credential, or entire hosting account. Some systems count requests within a time window. Others enforce burst limits, simultaneous request limits, or service quotas.
The response may include Retry-After, a header that tells clients when to try again. Its value can represent seconds or an HTTP date. Not every service sends it, and its absence does not rule out throttling.
Do not assume every capacity problem produces 429. Exhausted server resources can also cause timeouts or other error codes. The status alone cannot prove that your hosting plan needs an upgrade.
Capture One Failed Request Before Changing Anything
Start with the browser’s developer tools and open the Network panel. Capture one normal attempt at the affected action. Avoid repeatedly submitting payments, bookings, or other actions that create records.
Select the request showing 429 and record:
- The time, including timezone, and affected hostname.
- Request path and method, such as GET or POST.
- Response status, headers, and short error message.
- Any request identifier or security event reference.
- Whether the user had signed in and which action triggered the error.
- The affected network and approximate start of the incident.
A page can load successfully while a background request fails. Confirm whether the 429 affects the main page, an image, or an application programming interface (API). An API lets software exchange data.
Browser exports can contain cookies, credentials, and private form data. Remove secrets before sharing evidence, and use an approved secure channel.
Map the Layers That Can Apply Website Rate Limiting
Write down the request path before reviewing settings. A typical path runs from browser to content delivery network, then hosting server, then WordPress.
Content delivery networks (CDNs) serve content through distributed servers. A web application firewall (WAF) filters web requests and may operate within that service. Hosting systems may add another proxy, which forwards requests to the application server.
WordPress can also call an external API for payments, shipping, maps, or other functions. That creates a separate outbound request with its own limits.
- Edge service: Check CDN and WAF security events.
- Hosting layer: Review proxy, access, and account-limit logs.
- WordPress: Inspect security plugin and application logs.
- External dependency: Review integration errors and provider quota records.
Error-page branding and headers offer clues, not proof. An intermediary can forward another system’s response or replace its error page.
Locate the First Layer That Rejects the Request
Match the captured request against logs using its time, path, and identifier. Check timezone differences before concluding that an event is missing.
A matching WAF event that explicitly records a rate-limit rejection strongly points to the edge. If the request reaches hosting, compare the front-end response with the upstream application response. An upstream is the next server in the request path.
For Nginx deployments, administrators can consult the official Nginx documentation when reviewing proxy logs and rate-limit settings. Configuration determines both behavior and available evidence.
If WordPress records an external API 429, inspect how the integration handles that response. It may display an error inside a successful page or return a 429 to the browser.
Missing log entries do not prove that requests never arrived. Sampling, retention, disabled logging, or the wrong server can hide evidence. Ask the responsible provider to confirm the rejection point.
Check Who Shares the Rate-Limit Counter
Next, identify the counter’s scope. Ask whether the rule counts traffic by IP, account, credential, route, or another value.
Office users often share one public IP address. A per-IP limit can therefore block several people after one device creates a burst. A business VPN may group even more users behind the same address.
Proxy configuration can also create false grouping. If the application sees only a proxy’s address, it may count unrelated visitors together. Administrators should verify trusted-proxy settings and the recorded client address.
Never trust client-supplied forwarding headers from arbitrary sources. Incorrect trust settings can let visitors spoof their identity or bypass restrictions.
With approval, compare one ordinary request from another network after the waiting period. Use the result to understand scope, not to evade controls. Several integrations may also share one API credential and consume the same quota.
Separate Bot Traffic From Plugin and Browser Loops
Review traffic around the first rejection. Group requests by path, source, authenticated user, and client software identifier. Compare the burst with a normal period for the same business activity.
Bots may repeatedly request login, search, or expensive application routes. However, a familiar browser identifier does not prove human activity. Clients can change that value.
Legitimate code can generate similar bursts. Look for a page that polls too frequently, multiple open tabs, failed requests with immediate retries, or duplicate integrations.
Scheduled WordPress tasks can also trigger repeated outbound API calls. If the timing matches background jobs, review duplicate and overlapping WordPress schedules.
Test suspected plugin changes in staging when possible. Remember that staging may use the same live API credentials. Isolate those connections before testing, or the test could consume production quota.
Distinguish Hosting Limits From Resource Exhaustion
Ask the host for the exact policy name and enforcement layer. Request the limit’s scope, measurement window, observed usage, and rejection timestamps.
Hosting controls may apply to one site, a whole account, or shared infrastructure. Those scopes require different fixes. An account-wide request cap differs from limited processing capacity.
Check processor use, memory, queued requests, and application response times alongside the 429 timeline. High resource use can explain why a protective limit activates. It does not establish which component generated the response.
If requests stall without confirmed throttling, investigate WordPress PHP worker exhaustion as a separate capacity problem. PHP workers are processes that execute WordPress requests.
Keep website rate limiting and slow processing separate in your incident notes. Raising a request cap while requests remain slow can deepen an overload.
Choose a Narrow Fix for the Confirmed Cause
Once you know the rejection point and counter scope, choose the smallest effective change.
- External API limits: Reduce duplicate calls, queue work, and respect documented retry guidance.
- Retry storms: Use exponential backoff, which increases delays between attempts, plus random timing variation and a retry cap.
- Plugin request loops: Correct the trigger or roll back the implicated change after preserving evidence.
- False-positive firewall rules: Adjust the specific route, threshold, or authenticated-client policy rather than disabling protection.
- Abusive traffic: Apply targeted controls while monitoring effects on legitimate visitors.
- Verified hosting caps: Reduce demand or discuss a suitable limit change with the provider.
Do not automatically replay transactions after a 429. Confirm whether the operation completed and whether the API supports duplicate-safe retries.
Caching can reduce repeated work, but avoid caching private pages or transactional responses. The WordPress performance guidance provides broader optimization context.
Verify Recovery Across the Full Limit Window
Define success before making the change. Record the old setting, approval, rollback steps, and expected outcome. Change one relevant control at a time.
Wait for the documented reset period before a small test. A single successful reload does not prove recovery. Repeat the normal workflow at a controlled pace and watch the same logs.
- Confirm that legitimate users complete the affected action.
- Check that error rates fall without rising server load.
- Verify that queues drain instead of repeatedly retrying.
- Confirm that unrelated security protections remain active.
- Watch the next scheduled job or normal traffic peak.
Document the website rate limiting source, counter scope, trigger, and final correction. Keep monitoring lightweight so the checks do not create another burst.
Professional remote assistance may help when logs span multiple providers or production changes carry business risk. Tech Rescue Ops LLC can help correlate evidence and plan a controlled correction without broadly removing protective limits.