
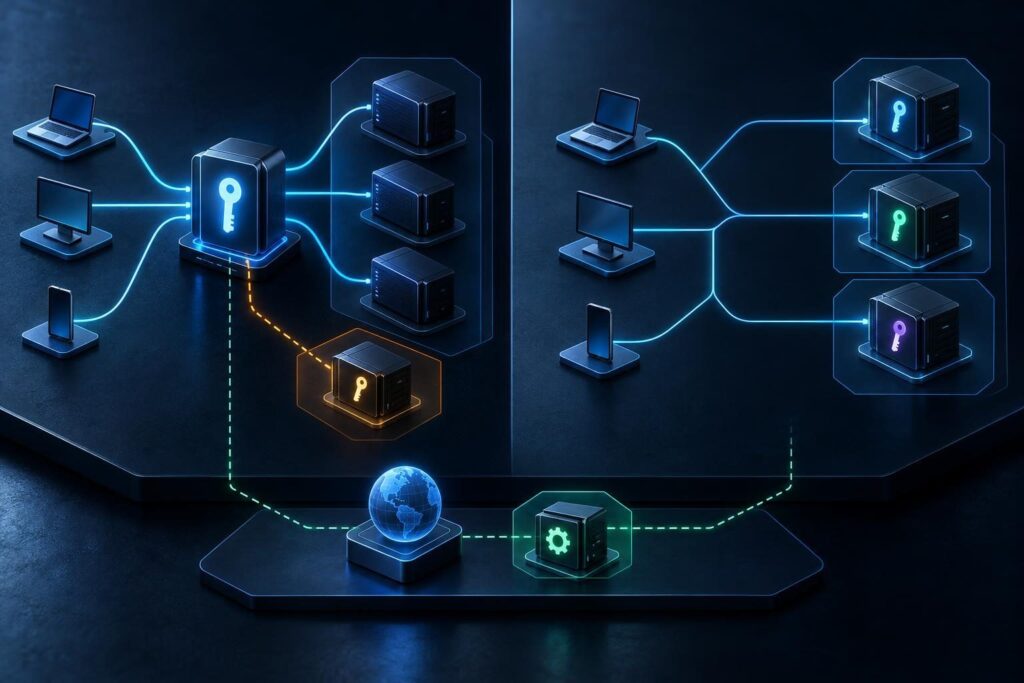
Choosing wildcard vs individual certificates is an operational decision, not just a purchasing choice. Both can protect connections with Transport Layer Security (TLS), commonly called SSL. The safer option depends on where keys live, who controls validation, and how reliably your team handles renewal.
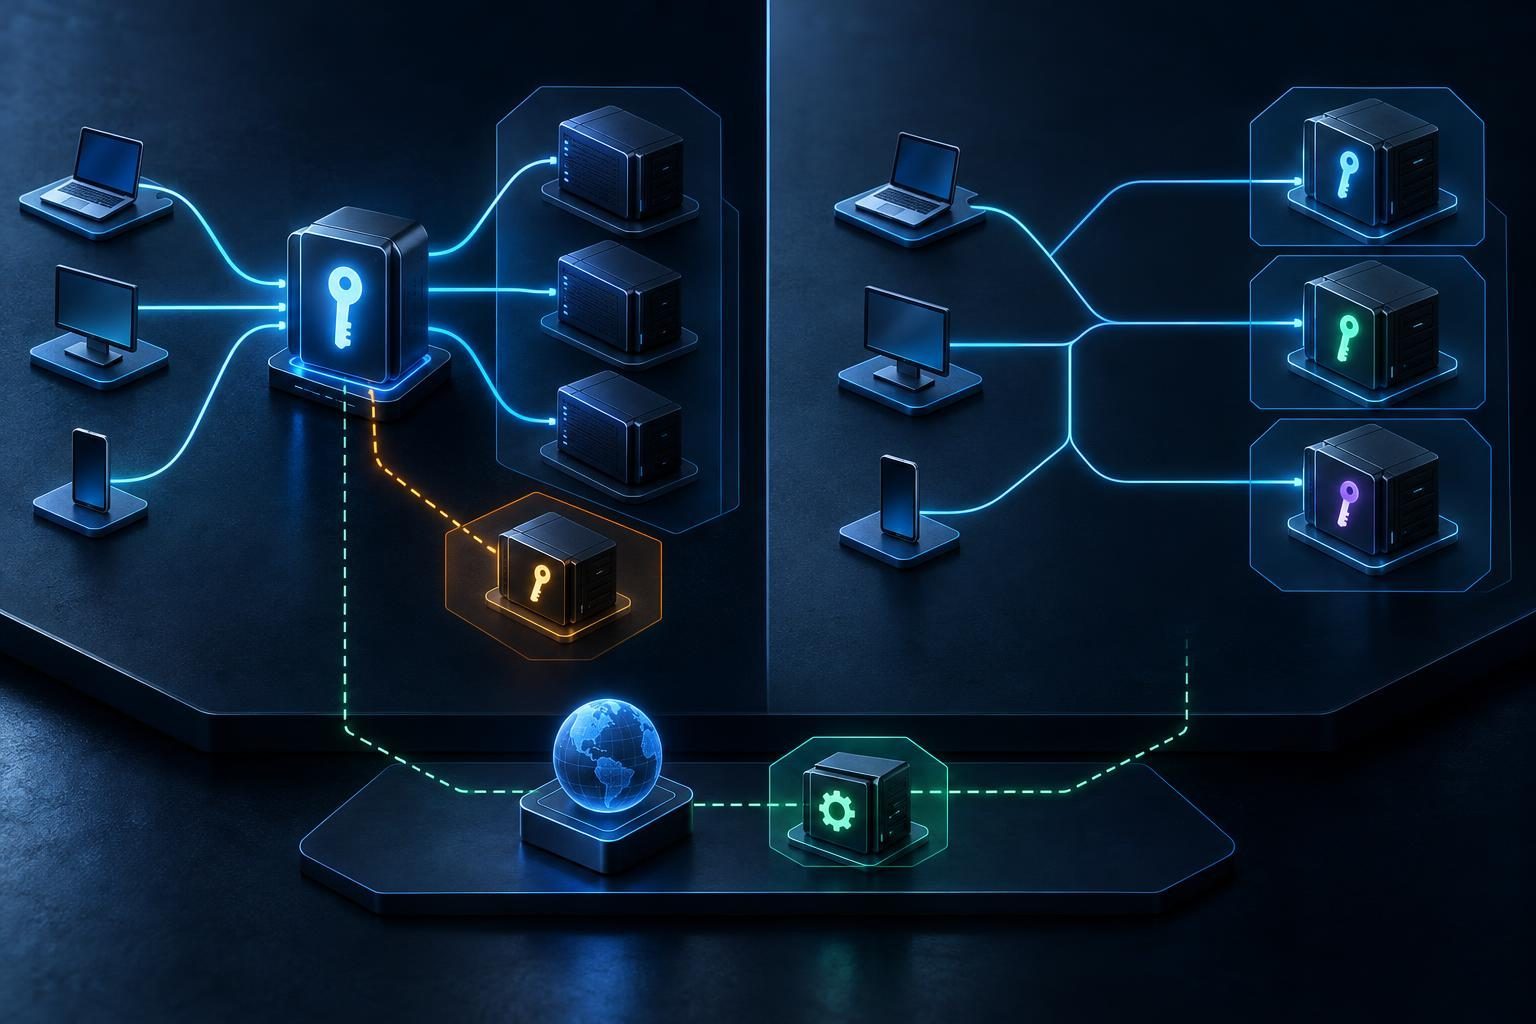
For most independently managed services, separate certificates and separate keys provide clearer isolation. A wildcard can work well at a tightly controlled shared entry point. Problems arise when convenience leads teams to copy one powerful key across unrelated systems.
What Wildcard and Individual Certificates Actually Cover
A certificate connects an approved hostname to a public key. Its matching private key lets the server prove its identity. Keep that private key secret.
A wildcard name such as *.example.com normally covers one label, including www.example.com and portal.example.com. It does not cover example.com or login.portal.example.com. A certificate can include the base domain separately.
An individual certificate usually means a certificate for one service or a small, explicit set of names. Technically, a certificate can list several names through its Subject Alternative Name extension. A large multi-name certificate can create shared risk similar to a wildcard.
Neither name format inherently provides stronger encryption. Protocol settings, key handling, and server configuration matter independently. Compare operational boundaries rather than assuming that a narrower name automatically means a safer deployment.
Compare Key Exposure and the Blast Radius
The blast radius means how much damage one failure can cause. With certificates, start by asking which names a stolen private key could impersonate.
A stolen wildcard key can support impersonation of matching names if an attacker can also intercept or redirect connections. Possession alone does not automatically redirect visitors or reveal every previously encrypted session.
Copying that key to several servers creates more places where attackers might obtain it. A weak staging server could expose the same credential that protects a production portal.
- Separate certificates and keys: Usually contain key compromise to the explicitly listed names.
- One shared wildcard key: Exposes every name within its scope and complicates replacement across all copies.
- Separate wildcard keys: Reduce key sharing, but each certificate still grants broad name coverage.
Separate files do not guarantee isolation. A shared administrator account, deployment system, or secret store may still expose every key. Review access paths as well as certificate names.
Wildcard vs Individual Certificates: Automation Changes the Answer
Manual renewal makes many small certificates feel expensive to operate. Reliable automation can reverse that comparison. Each service can obtain and renew its own narrow certificate without a technician tracking every expiration.
ACME, the Automated Certificate Management Environment protocol, automates certificate requests and validation. However, issuance is only one stage. A complete workflow must install the certificate, make the service load it, and verify the live connection.
A wildcard reduces the number of certificates only when services share it. That does not necessarily reduce deployment work. Every destination still needs secure delivery, activation, and verification.
Ask a provider these practical questions:
- Does automation generate a distinct private key for each intended boundary?
- Who receives alerts when validation or deployment fails?
- Can the system retry safely without requesting certificates repeatedly?
- Does monitoring inspect the certificate users actually receive?
- Can another technician operate the process without the original installer?
Judge automation by demonstrated recovery, not by a dashboard showing a successful certificate request.
DNS Validation Can Become the Larger Security Risk
Certificate authorities validate control before issuing a certificate. With Let’s Encrypt, wildcard issuance requires DNS-01 validation. This method publishes a special TXT record under an _acme-challenge name.
Non-wildcard certificates can also use DNS-01. Depending on the authority and deployment, other methods may prove control through a web endpoint or TLS connection. Consult the official Let’s Encrypt documentation for supported methods and current requirements.
Automated DNS validation often needs a DNS provider API token, a credential that allows software to change records. A token with full-zone access may also let an attacker redirect websites or alter email records.
Prefer credentials limited to the required records or validation zone where your provider supports them. Consider a dedicated validation service or delegated challenge zone. Confirm that your certificate client supports the proposed delegation method before rollout.
Do not place broad DNS credentials on every application server merely to simplify renewal. A narrow certificate backed by unrestricted DNS access can still create substantial risk.
During provider changes, include challenge records and automation access in your DNS migration plan. Moving ordinary website records alone does not preserve renewal capability.
Certificate Inventory Still Matters With a Wildcard
A wildcard does not replace an inventory. It tells you which names a certificate may cover, not where teams installed its private key.
Record enough information to locate every deployment and identify its owner:
- Service hostname, business purpose, and responsible team.
- Certificate names, issuer, expiration, and identifying fingerprint.
- Private-key storage location and authorized access roles.
- Validation method and credential owner, without recording secrets.
- Renewal client, deployment targets, and activation procedure.
- Monitoring destination and emergency replacement steps.
For shared certificates, list every copy, including standby servers and recovery systems. Otherwise, a forgotten copy can frustrate incident response.
Also distinguish where TLS ends. A reverse proxy accepts client connections and forwards requests to application servers. Keeping a wildcard only at that proxy limits distribution. However, it concentrates responsibility at the proxy and does not automatically protect the connection behind it.
Renewal Complexity Includes Failure and Recovery
One shared certificate can create a coordinated expiration event. If deployment fails everywhere, several services may break together. Separate certificates can spread failures, although shared automation or validation credentials remain common dependencies.
Evaluate wildcard vs individual certificates against a failed-renewal scenario, not just a normal month. Ask how many services depend on one job, one DNS token, or one person.
Test recovery on a noncritical service first. Use the issuer’s staging environment where available. Avoid repeated production requests that could encounter issuance limits.
- Confirm that monitoring detects a failed renewal or stale deployed certificate.
- Check whether the workflow preserves the currently working certificate when a replacement fails.
- Verify how each service loads a replacement without unnecessary disruption.
- Test every relevant frontend and network path after deployment.
- Document how to replace keys and revoke affected certificates after exposure.
Issuance success does not prove deployment success. Our guide to checking the live certificate path explains why a valid file can differ from what visitors receive.
Choose a Design That Matches Your Service Boundaries
Use the following comparison when evaluating a hosting provider, certificate service, or internal deployment plan. Compare total operating effort rather than certificate price alone.
| Environment | Practical Starting Point | Main Condition |
|---|---|---|
| Independent servers or separate vendors | Separate certificates and keys | Automate renewal without sharing broad credentials. |
| Many subdomains behind one controlled proxy | Consider a wildcard at the proxy | Keep the key confined and monitor every frontend. |
| Production and staging | Separate keys and access boundaries | Avoid giving staging credentials valid for production names. |
| Legacy devices with limited automation | Assess each device individually | Provide a documented renewal and emergency replacement process. |
A useful default is narrow certificates with independent keys wherever services have different owners or trust levels. Reserve wildcards for places where broad coverage serves a clear architectural purpose.
The decision between wildcard vs individual certificates should leave you with fewer uncontrolled dependencies, not merely fewer certificate files. Before committing, request a sample inventory, renewal test, credential scope, and replacement procedure.
Professional remote assistance may help when several hosts, DNS providers, or vendors share responsibility. Tech Rescue Ops LLC can review those boundaries and help plan certificate automation without spreading unnecessary access.