
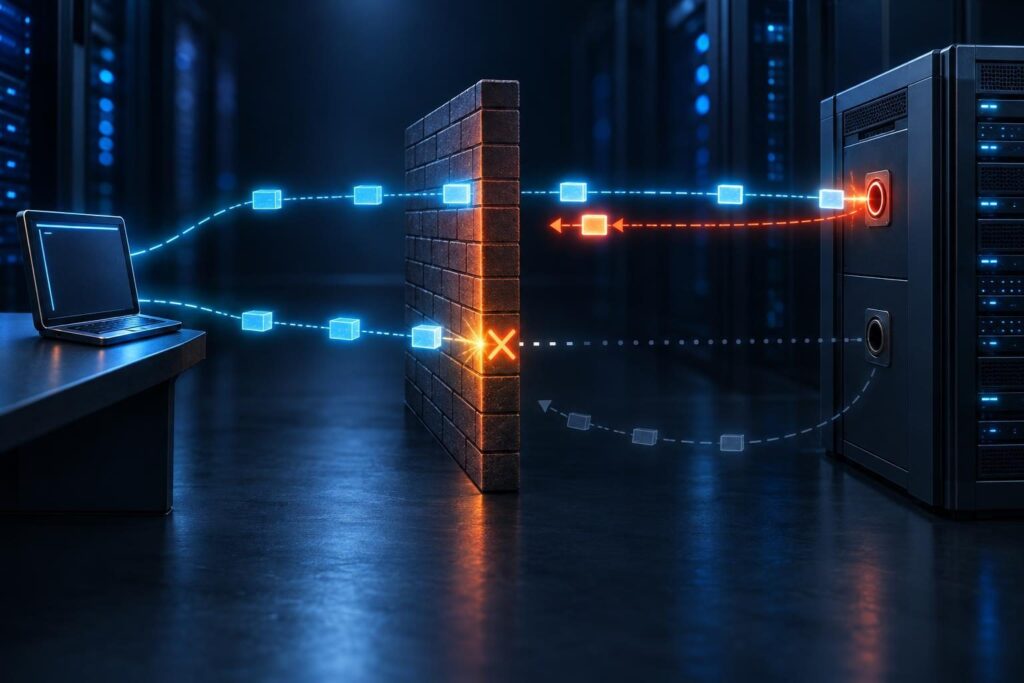
SSH connection errors tell you where to begin, but they rarely identify the faulty device alone. “Connection refused” usually means an active rejection reached your client. “Connection timed out” means the connection attempt did not finish within the allowed time. Neither message proves that your password, key, or SSH configuration caused the failure.
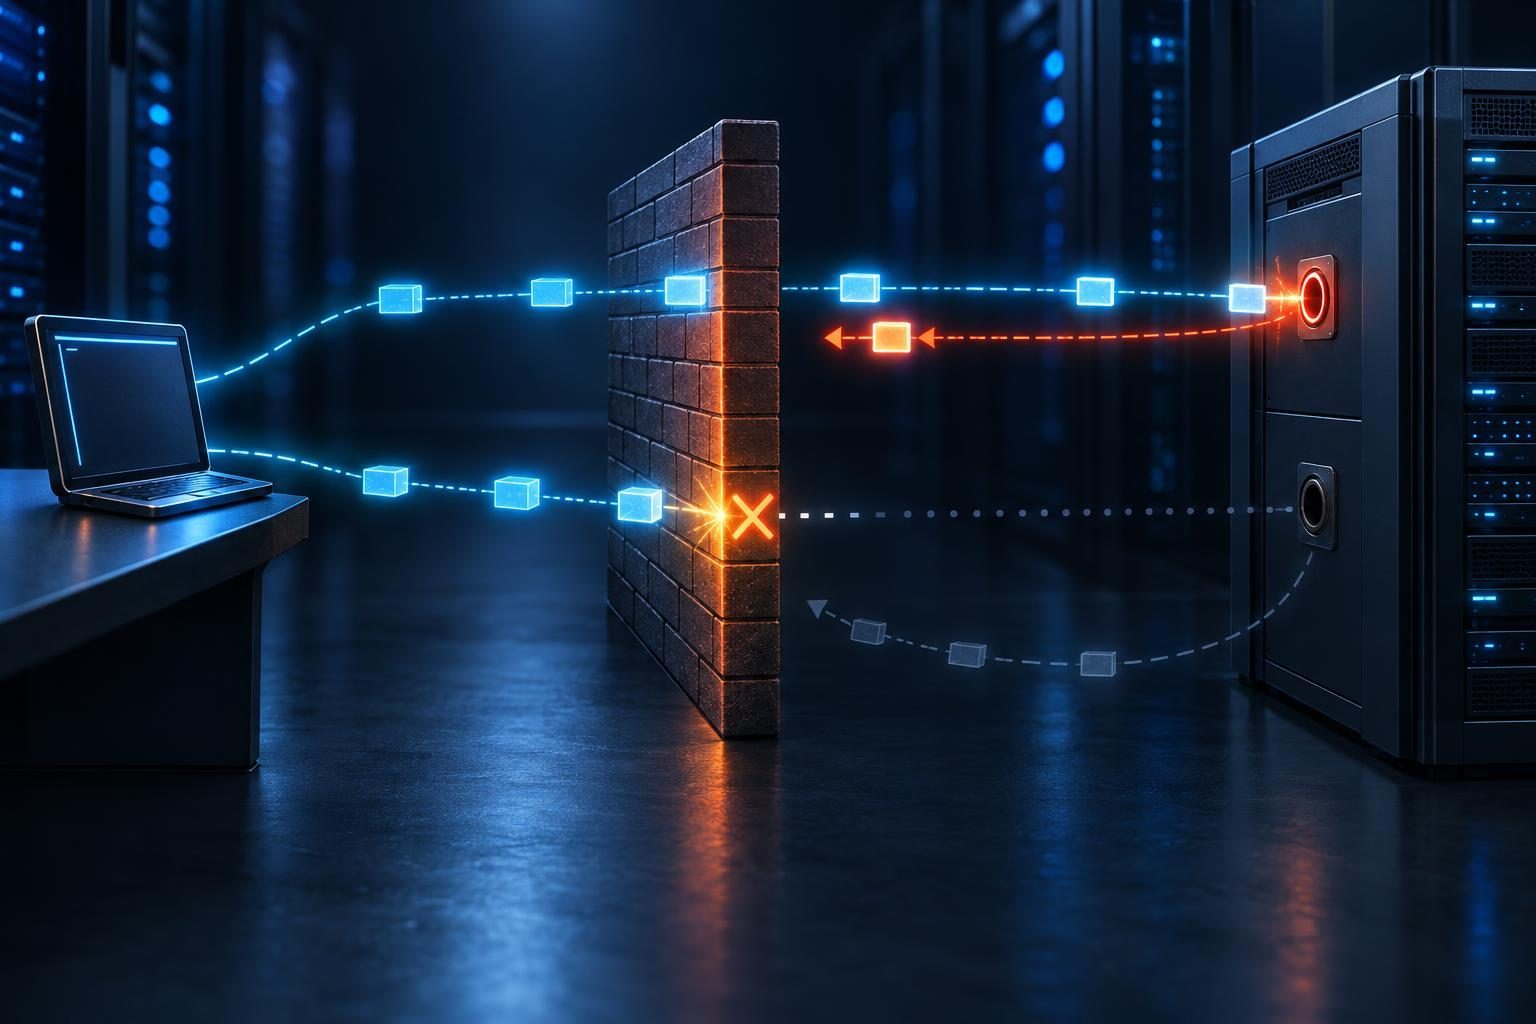
This guide compares the evidence behind those two outcomes. The goal is to distinguish a missing listener from filtering, routing, address translation, and source-specific blocking before making changes.
What Refused and Timed Out Actually Mean
SSH normally starts with a TCP connection. TCP is the transport protocol that establishes a reliable connection between your client and server. Only after that connection succeeds can SSH negotiate encryption and authenticate your account.
| Client result | Likely meaning | What it does not prove |
|---|---|---|
| Connection refused | A rejection, commonly a TCP reset, reached the client. | The intended server generated that rejection. |
| Connection timed out | The initial connection did not complete before the deadline. | A firewall definitely blocked the request. |
| Permission denied | SSH reached authentication and rejected the supplied credentials or method. | The network path failed. |
| Connection established, then stalled | TCP connected, but a later protocol stage stopped progressing. | The initial TCP connection timed out. |
A closed port commonly produces a refusal. However, a firewall can also reject traffic explicitly. Silent filtering often causes a timeout, but missing routes, an unavailable host, and broken replies can produce the same symptom.
Record the Exact SSH Destination Before Testing
Start by recording the hostname, resolved address, destination port, source network, and test time. Include whether the client uses a VPN, proxy, or jump host. These details make SSH connection errors comparable across tests.
For an authorized destination, a bounded diagnostic attempt can show the connection stage:
ssh -vv -o ConnectTimeout=10 -o ConnectionAttempts=1 -p 22 user@server.exampleReplace the example destination, account, and port with approved values. This command attempts a real login. Avoid repeated attempts that could trigger monitoring or account controls.
Read the destination address and port in the debug output. Client configuration may select a different port or route through another host. A hostname may also resolve to both IPv4 and IPv6 addresses.
If both address families should work, compare controlled attempts with -4 and -6. One family can fail while the other succeeds. Redact account names, internal addresses, and file paths before sharing debug output.
For Refused Connections, Verify the Listener
A listener is a process or socket waiting for incoming connections. Use an existing administrative session or provider console to inspect the destination server:
sudo ss -lntpThis inspection needs suitable privileges to show process details. The ss manual explains its socket display options.
- Find the intended SSH port, not just port 22.
- Check whether the listener uses IPv4, IPv6, or both.
- Confirm that its address matches the interface receiving your connection.
- Identify the owning process or socket manager.
A listener on 127.0.0.1 accepts local IPv4 connections, not connections to the server’s network address. A listener on one private address may not accept traffic arriving at another.
If nothing listens, inspect the SSH service status and logs. Unit names vary, commonly ssh or sshd. Some systems use socket activation, where systemd owns the listening socket.
Do not restart SSH blindly. Keep a recovery session open, validate proposed configuration changes, and confirm console access first. A running service status alone does not prove that the expected port accepts connections.
For Timeouts, Find Where the Packets Stop
Timeouts call for path evidence rather than immediate configuration edits. During one authorized connection attempt, compare observations at the client, firewall, and server.
A TCP connection begins with a SYN packet: a request to establish a connection. A listening server normally replies with SYN-ACK. Packet captures can reveal which part of that exchange disappears.
| Observation | Next question |
|---|---|
| No SYN reaches the server | Did routing, an upstream filter, or NAT send it elsewhere? |
| SYN arrives; no response leaves | Did host filtering or a local networking fault stop the reply? |
| SYN-ACK leaves; client never receives it | Does the return route cross a different gateway or filter? |
| Reset reaches the client | Which host or firewall generated the rejection? |
Capture only traffic you have permission to inspect. Limit the interface, address, port, and capture duration. Packet files can expose sensitive network details.
A successful ping does not prove SSH availability. Likewise, failed ping does not prove that the host is offline. Network controls can treat ping and TCP differently.
Separate Firewall Rejection From Silent Filtering
Firewalls can reject a connection or silently discard it. A rejection may create an immediate error. A silent discard often leaves the client waiting until its deadline.
Check controls at every relevant boundary: cloud security rules, perimeter firewalls, VPN policies, and the host firewall. Match logs against the actual source address, destination address, port, and timestamp.
An “allow” rule does not prove that traffic completed the path. Earlier rules, incorrect address objects, or another security layer may still block it. Compare rule counters before and after a single test when available.
Return traffic matters too. A server can receive your request but send its reply through the wrong gateway. Stateful firewalls track connections and may discard replies they cannot match. Our guide to tracing blocked return traffic explains that evidence in more detail.
Do not disable all filtering to test access. Prefer a narrow, approved rule with a clear rollback plan when evidence justifies a change.
Check NAT and Port Changes as a Pair
Network address translation, or NAT, can map a public address and port to a different internal destination. For example, an approved public port might forward to internal port 22.
Document both sides of that mapping. The client must use the external port, while the server must listen on the internal target port. A stale forwarding rule can reach a closed port and produce a refusal.
Other mistakes produce silence. The forward may target an old private address, or an upstream router may never pass the connection downstream. Provider-managed NAT can also prevent direct inbound access.
Test external forwarding from an authorized external network. Testing the public address from inside may depend on NAT reflection, which not every network supports.
Use upstream NAT checks when traffic never reaches the firewall you manage. Changing the SSH port does not fix a missing route or replace access controls.
Identify Source-Specific Bans and Service Availability
If one administrator connects while another cannot, compare their source addresses and paths. Different VPN exits, IPv6 use, and shared public addresses can explain different results.
fail2ban watches logs and applies configured ban actions after matching activity. Its actions vary: some discard packets, while others reject them. Therefore, fail2ban can contribute to either a timeout or an immediate refusal.
Inspect the relevant jail status, ban records, and firewall action. Confirm the source address as the server sees it. Do not clear every ban or disable protection merely to test a theory.
Service availability can also change between attempts. Correlate failures with boots, service exits, maintenance, and resource pressure. If SSH alternates between listening and stopping, inspect that timeline rather than treating each result as a separate network fault.
Authentication throttling or early disconnects may occur after TCP connects. Check debug output carefully before classifying those events as initial connection failures.
Turn SSH Connection Errors Into an Evidence-Based Handoff
Collect a compact record before escalation:
- Exact error and the stage where the attempt stopped.
- Source address, destination address, port, and address family.
- Timestamp with time zone and relevant recent changes.
- Listener details and SSH service status.
- Matching firewall logs or narrowly scoped packet observations.
- Results from one known-good comparison path, if available.
The practical rule is simple: refusal suggests an active response; timeout suggests an incomplete exchange. Locate that response or missing exchange before changing credentials, ports, or security policies.
Professional remote assistance may help when several network owners or security layers share the path. Tech Rescue Ops LLC provides remote server support to correlate evidence and plan controlled changes, provided suitable access and recovery options exist.